Fixed scope
Microsoft 365 security check
A quick, fixed-scope starting point: a read-only check of your Microsoft 365 security basics, with your top findings and clear next steps.
Our services
We help regulated financial firms take up Copilot and other AI tools on Microsoft 365, with the security, evidence and supplier oversight UK regulators expect. You get a fixed scope, plain English and a written plan.
For brokers, wealth managers, small insurers, payment and fintech firms, and technology suppliers to EU financial firms.
For accountants, solicitors, financial advisers and other professional firms of 10 to 50 staff.
A quick, fixed-scope starting point: a read-only check of your Microsoft 365 security basics, with your top findings and clear next steps.
Our servicesA monthly check that your settings haven't drifted, a quarterly review and help with your Cyber Essentials renewal. Protect adds management of your agreed security policies. Neither is a 24/7 service.
Our servicesEach week, what the latest UK scams and security news mean for your firm, in plain English. Follow our scam alerts on Instagram @allmytech.uk.
Read the round-upEach starts with a short, fixed-scope check and a clear answer on what to fix first.
Your team wants Copilot and AI tools, and your regulator expects you to know where your important services and suppliers sit. Microsoft Copilot can surface anything a user already has access to, so permissions and sharing need checking first. We find out which rules apply to you and what to get ready before the new UK incident and third-party reporting rules start on 18 March 2027.
Our servicesYou pay for Microsoft 365 security features, but you're not sure which are switched on and enforced.
Our servicesThe Microsoft Sentinel bill keeps rising, alerts are noisy, and nobody is quite sure what is really covered.
Our servicesA 30-minute call, then a short written scope.
Read-only access for the agreed dates, removed when the check ends. We change nothing.
A plain-English summary rated red, amber or green, and a 30/60/90-day plan your team or IT provider can act on.
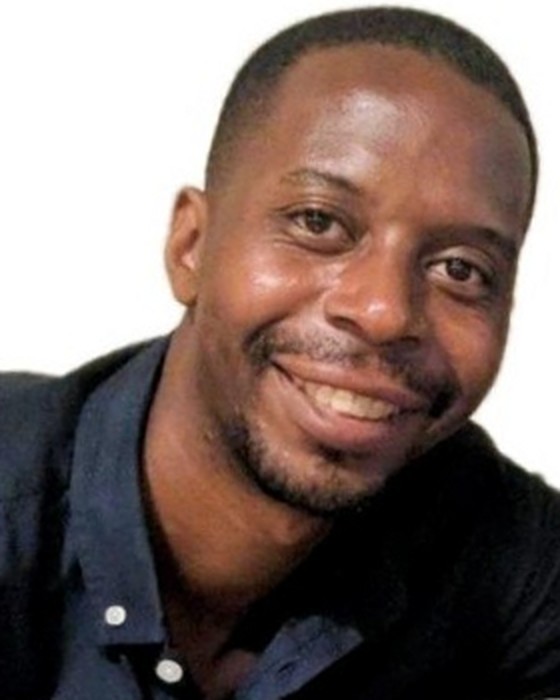
Wayne Reid, Principal Consultant, leads our work on Microsoft 365, Purview and Sentinel security, operational resilience evidence, and AI governance and Copilot readiness, drawing on more than 15 years in IT across financial services, retail and the public sector.
Senior-led from first call to final report. Every finding is reviewed before it reaches you.
Something else on your mind? Ask us on a call, or email info@allmytech.co.uk.
No. We give an independent second look and work alongside them. Findings go to whoever will act on them.
Not during a check: access is read-only and removed when the check ends. Changes happen only in a project or retainer, and only with your approval.
No. We work business hours, UK-based, and say so up front. We can work alongside a 24/7 provider.
Access is read-only, limited to the roles the check needs, and removed when it ends. Findings are stored encrypted and deleted on the date agreed in your engagement letter.
Each piece of work has a fixed fee. Ask for the one-page brief, or book a 30-minute call.
If you are UK-only, usually not. Your rules come from the FCA and, for some firms, the PRA. DORA can apply directly to an EU-licensed entity in your group. If you supply ICT services to EU financial firms, it usually reaches you through their contracts with you. We'll tell you which applies on a 30-minute call.
We'll tell you plainly whether we can help, and if we're not the right fit, we'll say so.